Security
Chat sits on your website and sees your customers, so it gets the same scrutiny as the rest of your stack. Here is what we actually do, and what we do not.
Found a vulnerability? Email security@talkfront.app. We confirm receipt within two working days.
Keeping customers apart
One database, with isolation enforced in the query layer rather than left to whoever writes the next feature.
Every row is owned
Anything belonging to a workspace carries its workspace id, and a global scope applies it to every query automatically.
URLs cannot be walked
Records with their own pages are addressed by UUID rather than a sequential id, and route binding is scoped to the workspace, so guessing an id gets you a 404 rather than someone else’s conversation.
API tokens are scoped
A token belongs to one workspace and cannot read outside it.
The widget on your site
The part that runs on your pages, in front of your customers, where the blast radius of a mistake is largest.
It runs in its own frame
The chat is an iframe on our origin. Your CSS and JavaScript cannot reach into it, and it cannot reach into yours.
Messages are text, never HTML
Message bodies are rendered as text in the widget and in the inbox. A pasted script tag stays a pasted script tag.
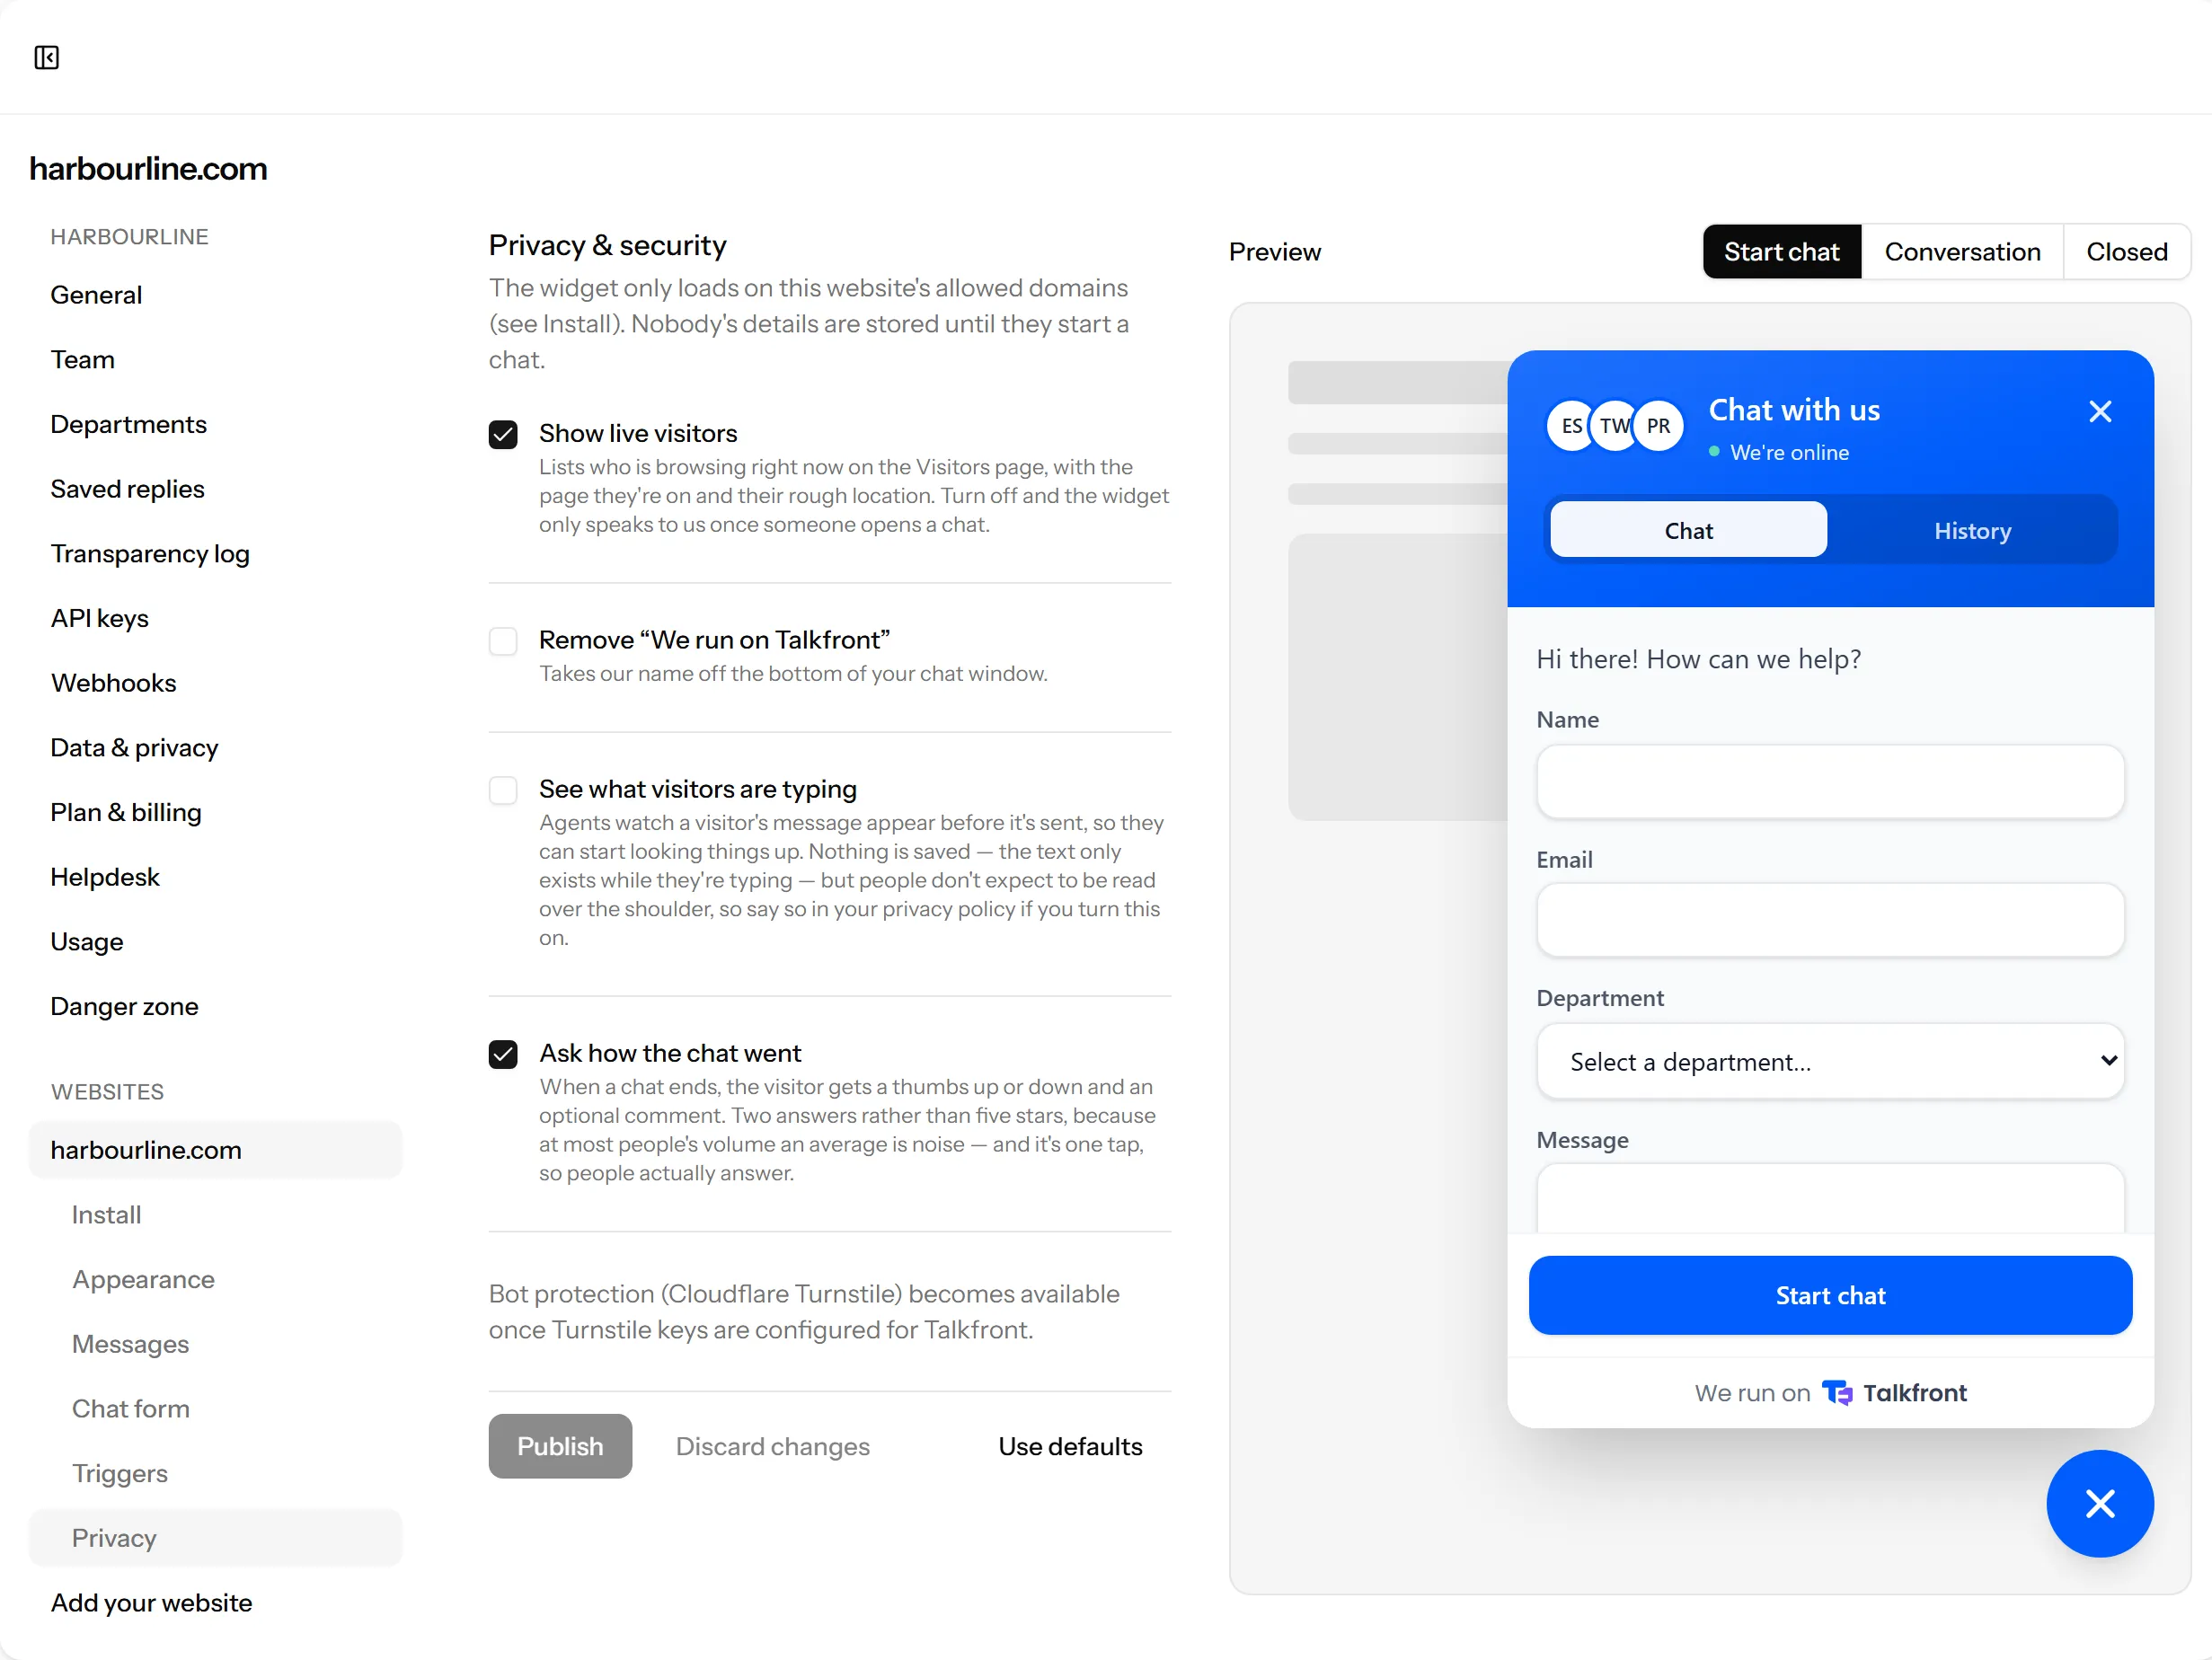
The site key is public by design
What protects you is the per-site domain allowlist, enforced on every request and in the frame’s own frame-ancestors policy, plus rate limiting. A key on its own reads nothing.
Visitor tokens are hashed
The token that keeps a visitor’s conversation across page loads is stored hashed, not in the clear.
Identity can be proven
Sign the user id on your server with your site secret and the contact is marked verified. Unsigned details are accepted but never merged into a verified contact, so nobody reads someone else’s history by editing the snippet.
Bot protection on forms
Pre-chat and offline forms can require a Cloudflare Turnstile check, which stops overnight spam without a puzzle.
Accounts and access
Most breaches are a password, not a zero day.
Two-factor and passkeys
Agents can secure an account with an authenticator app or a passkey.
Owners can require it
A workspace owner can make two-factor mandatory for every member.
Roles
Owner, admin and agent, with deletion of workspace data restrictable to owners.
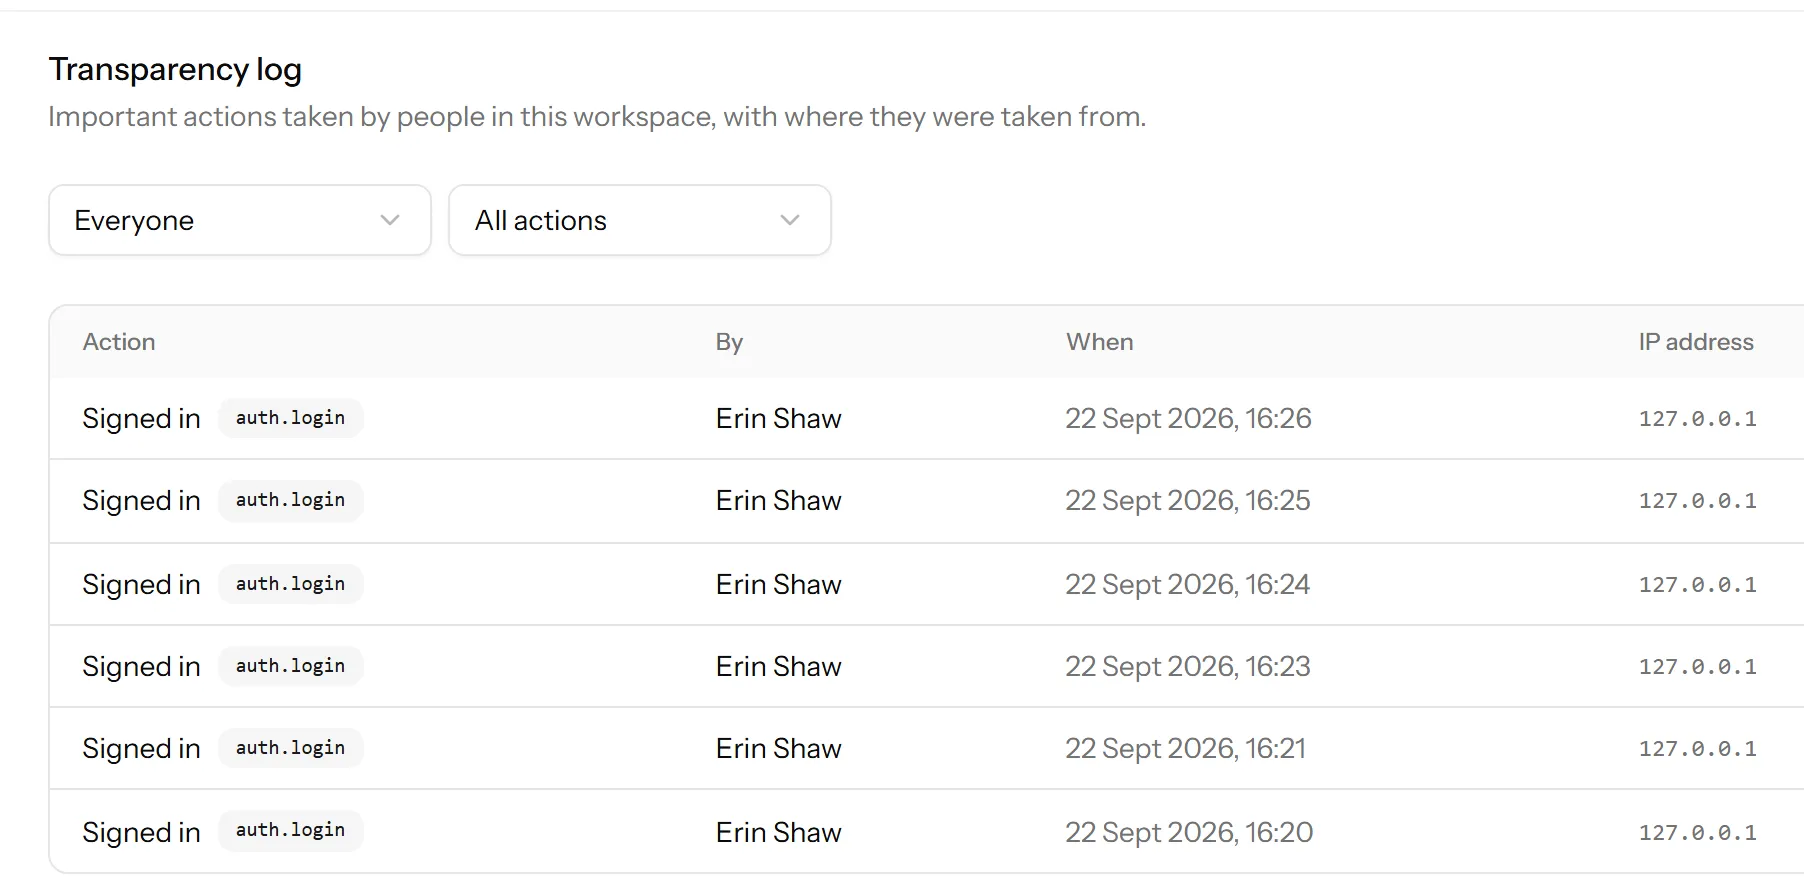
A log of who did what
The transparency log records member actions with timestamps and IP addresses, and it is filterable, so an audit is a search rather than an investigation.
Single sign-onSoon
SAML and OIDC for Business workspaces.
Your data
Where it is, how long it stays, and how to get it out.
Hosted in Europe
Application, database and backups are in Europe. Conversations do not travel through a third-party messaging service on the way to your inbox.
Encrypted in transit
TLS everywhere, including the WebSocket connection that carries messages.
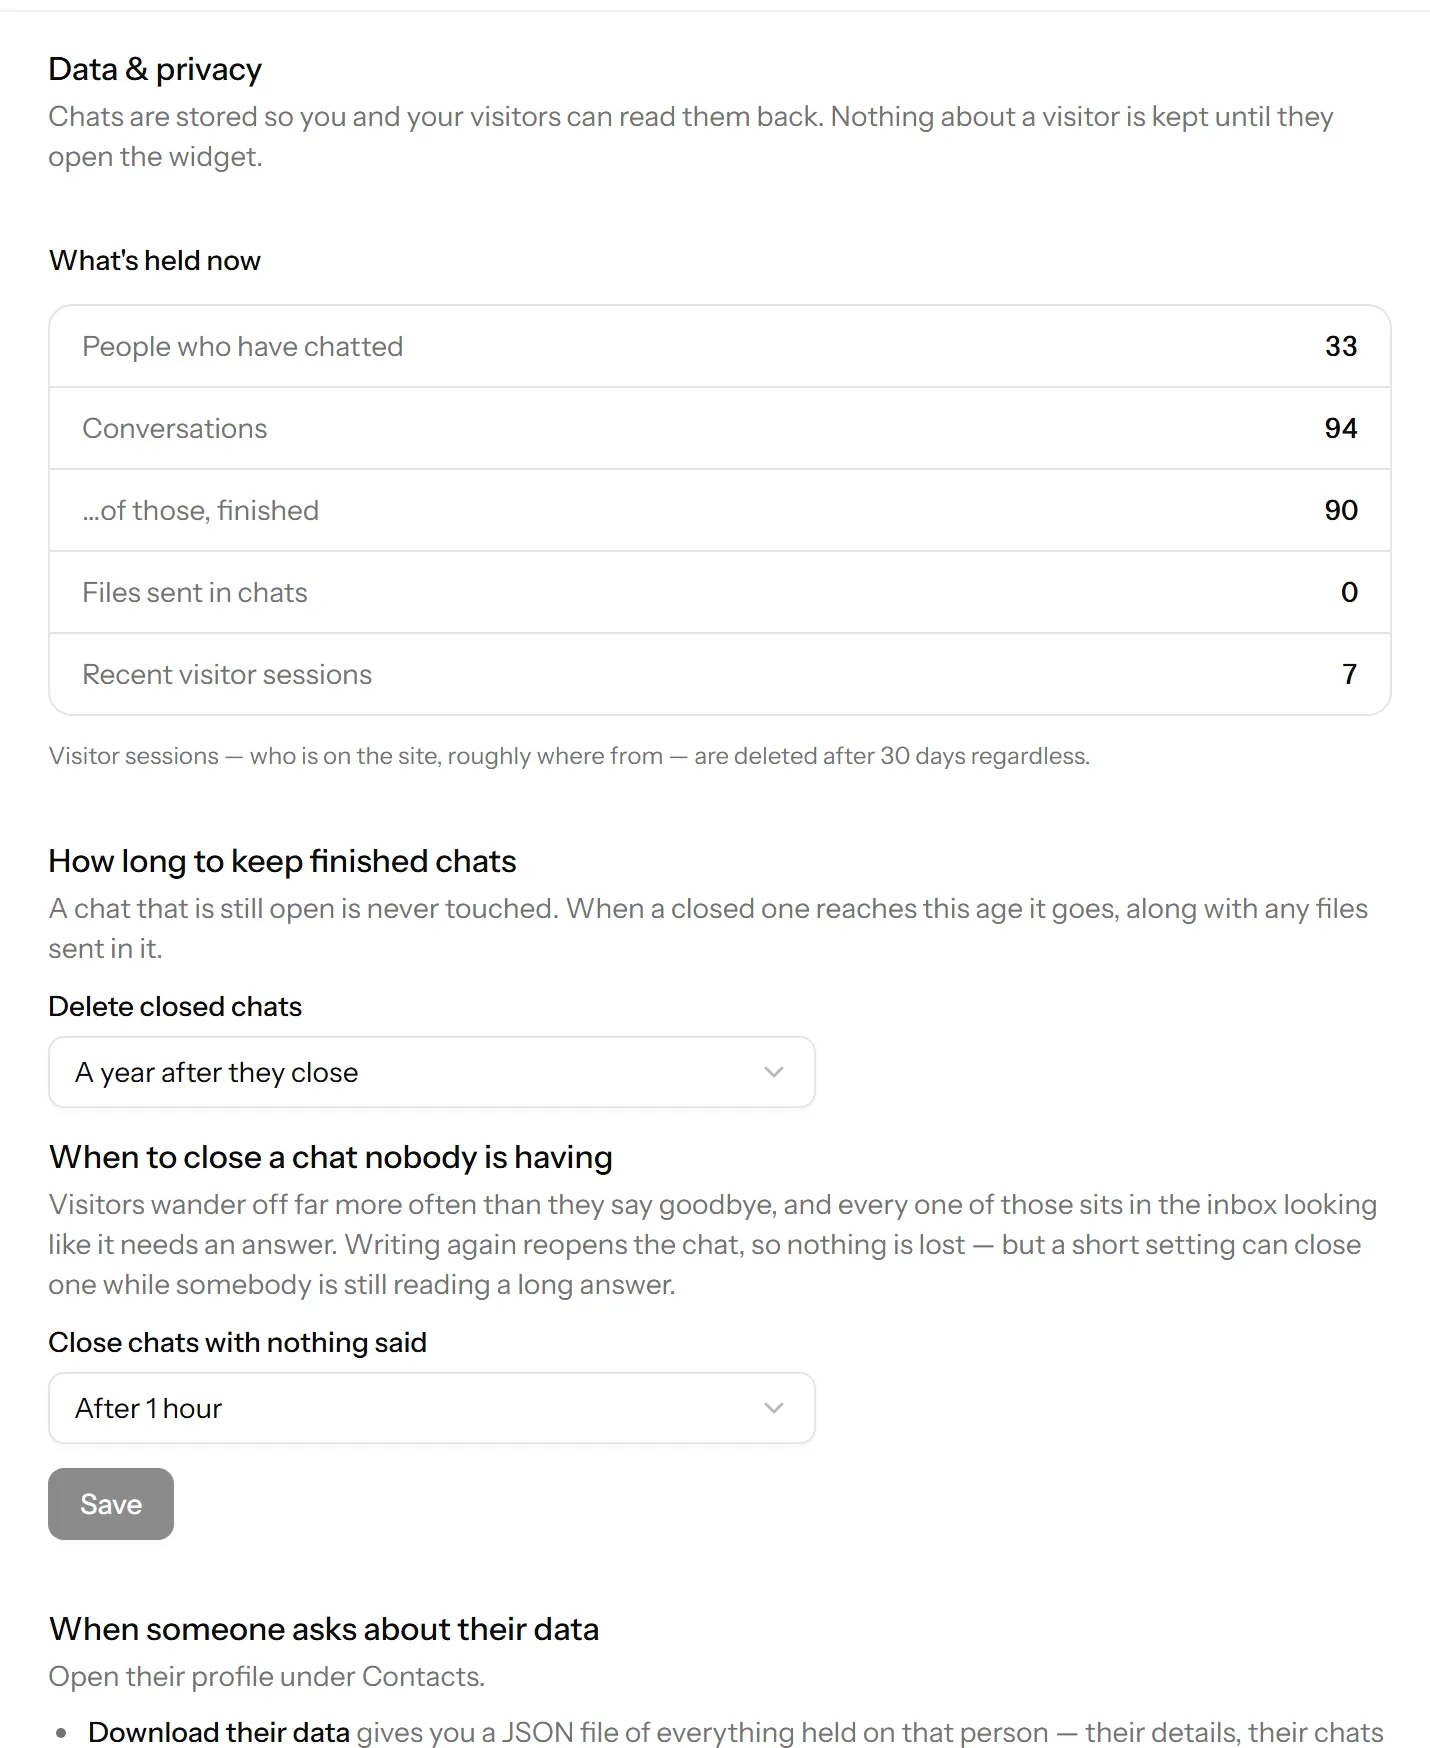
Store nothing until a chat starts
A per-site setting: a visitor who never opens the widget leaves no record behind.
We never see card details
Payments go through Stripe. Card numbers do not reach our servers.
Export and erase
Download everything held about one person, or erase it including their files and visit history, on any plan. Contacts also export to CSV in bulk.
Reporting a vulnerability
Email security@talkfront.app with enough detail to reproduce it. We confirm receipt within two working days and tell you what we are doing about it.
Please do not run automated scanners against production, access an account that is not yours, or read another customer’s data to prove a point. If you need a workspace to test in, ask and we will set one up.
We have no bug bounty. We will credit you publicly if you want it, and we will not threaten you for telling us.
What reviewers usually ask
If your questionnaire has something not covered here, send it to privacy@talkfront.app and we will answer it properly rather than in marketing language.
Can we have a data processing agreement?
Yes. Email privacy@talkfront.app and we will send one. For the chats your visitors have with you, you are the controller and we are your processor.
Do you have SOC 2 or ISO 27001?
No. We are a small company and neither certification would be honest to claim at this size. What we can give you is a straight answer to any question on this page, a signed DPA, and the architectural detail behind any control here.
Where exactly is the data?
In Europe. If you need the specific region and provider named in writing for a supplier questionnaire, ask and we will put it in writing.
Do you use our conversations to train models?
No. Your conversations are not used to train anything, ours or anyone else’s, and they are not sold or shared for advertising.
What happens if there is a breach?
We tell you. Where UK GDPR requires it we notify the ICO within 72 hours, and we contact affected customers directly rather than waiting for them to read a status page.
Start talking to your visitors today
Create a workspace, paste one line into your site, and answer your first chat in a few minutes.
Free plan, no card needed.